APK basics
An APK (Android Package Kit) is the standard file format Android uses to distribute and install apps.
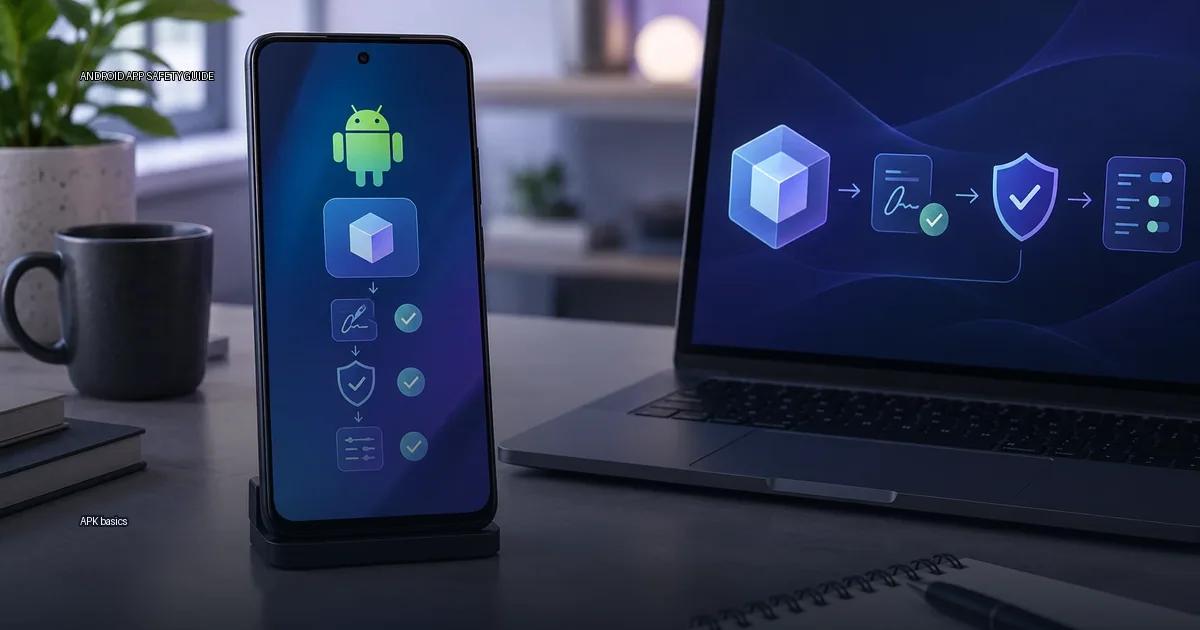
An APK (Android Package Kit) is the standard file format Android uses to distribute and install apps. It is a ZIP archive containing compiled code, resources, the AndroidManifest.xml that declares permissions and components, and the developer’s signing certificate. Understanding APK basics means recognizing that the format itself is not dangerous. The risk lives in who built the file, what they put inside it, and whether its cryptographic stamp matches the one the developer used for previous updates.
When you download from the Play Store, you receive an APK generated from an Android App Bundle (AAB). Since 2021, Google Play has required new apps to publish as AABs, a publishing format that lets the store produce optimized APKs for each device configuration. When you download an APK from a website, you are getting a universal or split APK that may not match your device’s architecture, which can cause installation failures or missing features. The four focused guides own the detail on finding, verifying, installing and locking down apps; the material below gives you the framework to understand every step that follows.
APK basics: How Android handles APKs
Android is the operating system that manages app installation, file access and permissions. It does not enforce a single app store. The default setting blocks “unknown sources,” but that is a generic toggle, not a quality filter. When you enable it, you tell the OS to allow installation from outside the default store, but you do not bypass the system’s cryptographic checks. Android still verifies that an APK is signed before installing it and refuses to install an app signed with a different key than an existing update.
An app’s compatibility is determined by its targetSdkVersion and minSdkVersion. The Android Developers documentation explains that targetSdkVersion indicates which API level the app was tested against, and newer Android versions apply compatibility behaviors based on that value. An APK that targets an older SDK may install on a newer OS but can lack modern security patches. When an APK targets a very old SDK, the OS may show a warning or block installation entirely, depending on the Android version. The Play Store enforces a minimum target SDK for new apps and updates; sideloaded files are not subject to that enforcement, so you carry the risk.
The signing model
APK files are signed with a digital certificate. The signature is the core of Android’s trust model: it proves the file was signed by the same key as previous versions of the app, and it lets the system reject updates that were not signed by that key.
- Signature Scheme v1 (JAR signing) is legacy and only covers individual files inside the APK.
- Signature Scheme v2 covers the whole file and resists tampering more effectively.
- Signature Scheme v3 adds key rotation.
A valid cryptographic stamp means the file came from the same developer who signed the previous version, not that the developer is a known good actor. A matching hash proves file identity and a matching signing certificate supports publisher continuity; neither proves an app is harmless.
How Play Protect fits in
Play Protect is Google’s on-device and cloud-based scanner. It checks apps before and after installation, but it does not continuously monitor sideloaded apps the way it does Play Store apps. A clean scan is one layer among several; it is not a guarantee of safety. Keep Play Protect enabled. If you encounter a harmful-app warning, do not look for an “Install anyway” workaround; stop the installation and re-evaluate the file’s source and integrity.
Permissions as a second layer
Android’s permission model asks you to grant access to sensitive data and features. An app that requests more than its core function needs is a red flag regardless of the store. OWASP MASVS provides a framework for evaluating mobile app security, but it is aimed at developers and auditors, not end users.
The decision that matters most
Sideloading is not inherently dangerous. The risk is determined by the source of the file and the integrity of its signature. The most common mistake is assuming all non-Play-Store files are malware, when the real danger is downloading from unofficial aggregators or ignoring a mismatched cryptographic stamp. Use this checklist before you install anything outside the Play Store.
Before you install: a 3-point checklist
- Source. Get the file from the developer’s authenticated channel. Never use unofficial APK aggregators, modded packages, cracks or paid-app copies. A checksum alone does not prove trust; verification must begin with the publisher’s own distribution point.
- Signature. Confirm the stamp on the file matches the developer’s key. Android will reject an update signed with a different key, but you should catch the mismatch before you try to install.
- Permissions. Compare what the app asks for against what its core function actually needs. Reject any app that demands more than that.
When you can skip the worry
- You are installing an update from the same developer whose app is already on your device, and the signature matches.
- You are using a reputable, developer-run distribution channel (such as an official GitHub releases page) and you have verified the file hash against the publisher’s published value.
When you should stop and verify
- The file comes from a forum, a file-sharing site or a third-party store you have not researched.
- The app requests permissions that have no clear connection to its stated function.
- Android shows a signature mismatch warning during installation.
Where the other guides take over
The four focused guides own the step-by-step instructions.
- Find apps safely walks you through locating a developer’s authenticated channel and avoiding repackaged files.
- Verify an APK covers hash verification, signature inspection and tools that flag tampering.
- Install and update safely gives you the exact sequence for sideloading and keeping apps current without the Play Store.
- Permissions and privacy shows how to audit what an app can access and how to lock down sensitive data.
Quick-reference definitions
- APK: a single file containing the code and resources of an Android app, similar to a .exe on Windows, but with a cryptographic stamp that ties updates to the original developer.
- App bundle (AAB): a publishing format that Google Play uses to generate a small, optimized APK for each device, instead of one file that fits all.
- Signature: a cryptographic stamp from the developer’s private key. If the stamp does not match the one on the installed app, Android refuses to update it.
- Play Protect: Google’s on-device scanner that checks apps for known malware before and after installation. It is not a guarantee.
- Permission: a declared capability the app requests from the operating system, such as camera, location or contacts. You must grant it before the app can use it.
The format itself is not dangerous. The risk lives in who built the file, what they put inside it, and whether its cryptographic stamp matches the one the developer used for previous updates.
More in this guide
Read next
-
 What an APK file is
An APK (Android Package Kit) is the file format Android uses to distribute and install apps.
-
 APK vs Android App Bundle
If you have ever obtained an Android app outside the Play Store, you have likely seen two file formats: APK and Android App Bundle (AAB).
-
 Android app signatures
When you install an Android app, you are not just copying files onto your device. You are accepting a chain of identity checks that starts with a cryptographic signature.
-
 Versions and compatibility
When you install an Android app outside the Play Store, three technical details decide whether the install succeeds and whether the file is what its creator actually shipped: the version…
- Inside an APK: manifest and resources Inside an APK: manifest and resources. Walk through the AndroidManifest.xml, resources.arsc, and the res/ folder to show how an app declares its identity, permissions, and UI.
-
 Find apps safely
Every Android user eventually faces the same question: where can you get an app without putting your phone at risk? The honest answer is simpler than most advice suggests.